Cybersecurity
should not be
guesswork.

Can you answer the questions that matter:Where are you exposed?What can actually be exploited?What should you fix first?SIT maps your IT environment, validates what can actually be exploited and shows what matters most. With recurring automated control and expert support, you fix the right risks and drive risk down over time.

Security team analyzing technical cyber exposure

This is what the cyber threat landscape looks like
in practice.

New vulnerabilities, exposed services and changing attack methods keep the risk picture moving. These examples show how technical exposure has produced real operational consequences.

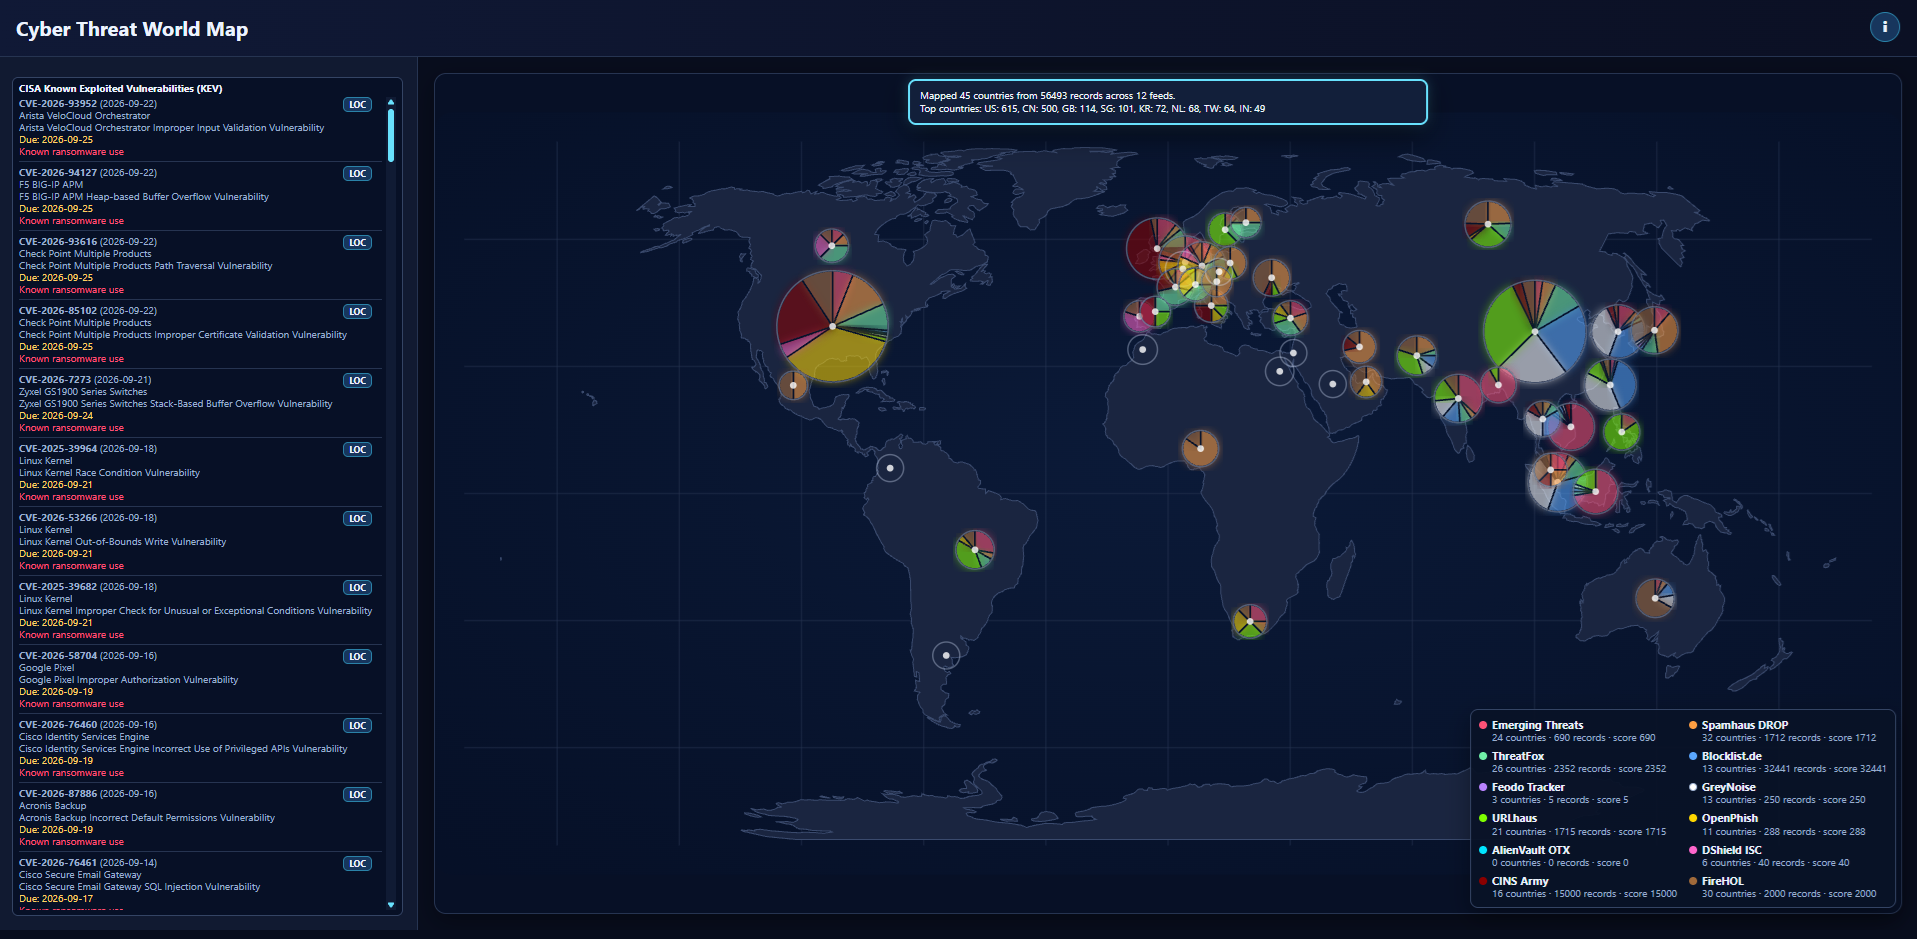
Cyber Threat World Map

Known firewall and VPN vulnerabilities became the way in.

Ransomware actors exploited vulnerabilities in internet-facing edge devices. The result was data theft, encryption and disruption.

SIT Xternal shows the external exposure. Threat matching elevates actively exploited vulnerabilities. The next control verifies that the exposure is gone.
An unpatched remote-support platform became an initial foothold.

Vulnerabilities in remote-support software were used for code execution and further access. The risk then spread through environments that depended on the service.

SIT Appliance identifies product and version. Threat matching connects new threats to the environment you actually run. The next control verifies that the risk is gone.

Several weaknesses became more dangerous together than on their own.

Attackers chained multiple weaknesses to gain access, execute code and move further into the environment.

SIT shows the attack chain and raises the priority when several weaknesses combine into a greater risk than each finding in isolation.

Better security decisions start with
seeing reality as it is.

An accurate risk picture starts with an accurate view of your IT environment.

SIT automatically and repeatedly maps what is actually present on your network: systems, services, products and versions. This information is matched against a broad vulnerability data set to give you as complete and accurate a view as possible of the vulnerabilities that affect your environment.

Security and management team with IT infrastructure

More findings are not enough.
You need to know what to fix first.

SIT finds broadly. Then we determine what actually matters most.

Reachability, exploitability, known exploits, active exploitation, attack chains and business criticality are weighed together. The result is Top Priorities, showing which Critical and High risks you should fix first.

More data is not the goal.Better decisions are.
Security team analyzing technical exposure and prioritizing the risks that matter most
Broad visibility. Clear priorities.Find widely. Fix the risks that matter first.

Track risk
as it moves down over time.

Recurring automated control makes change visible. See what is new, what remains and what has disappeared after corrective action. The next control verifies the effect so you can track and demonstrate how risk is being driven down over time.

Security team reviewing recurring control and risk trend over time
Map → Prioritize → Fix → Verify → Track12 scans per year · Delta Report · Risk Score over time · Continuous threat matching
SIT Appliance in a local IT environment

No information leaves your network.

SIT Appliance analyzes your internal IT environment locally. Scan results, analyses, reports and history stay inside your network. Scanning is agentless and unauthenticated, no software is installed on your servers or endpoints, and no privileged accounts are required.

All analysis stays localSIT Appliance runs internal analysis inside your network.
AgentlessNo software needs to be installed on your servers or endpoints.
UnauthenticatedSee what is visible and reachable from the network without relying on credentials.

Developed in Sweden.

SIT is a Swedish cybersecurity company, and our product technology is developed in Sweden. You stay close to the technology, the people developing it and the expertise that helps you interpret results and prioritize the right actions.

Keeping product development and expertise in Sweden also contributes to Swedish digital resilience. Internal analysis runs locally inside your network and does not depend on an external cloud service. That gives you greater control over where security information is processed and reduces unnecessary external dependencies.

Cybersecurity developed in Sweden and Swedish digital resilience

Technical control that strengthens
systematic cybersecurity.

Use recurring technical control, prioritized remediation and a trackable risk trend as concrete input to your security program. SIT supports the technical areas you can observe, verify and follow over time.

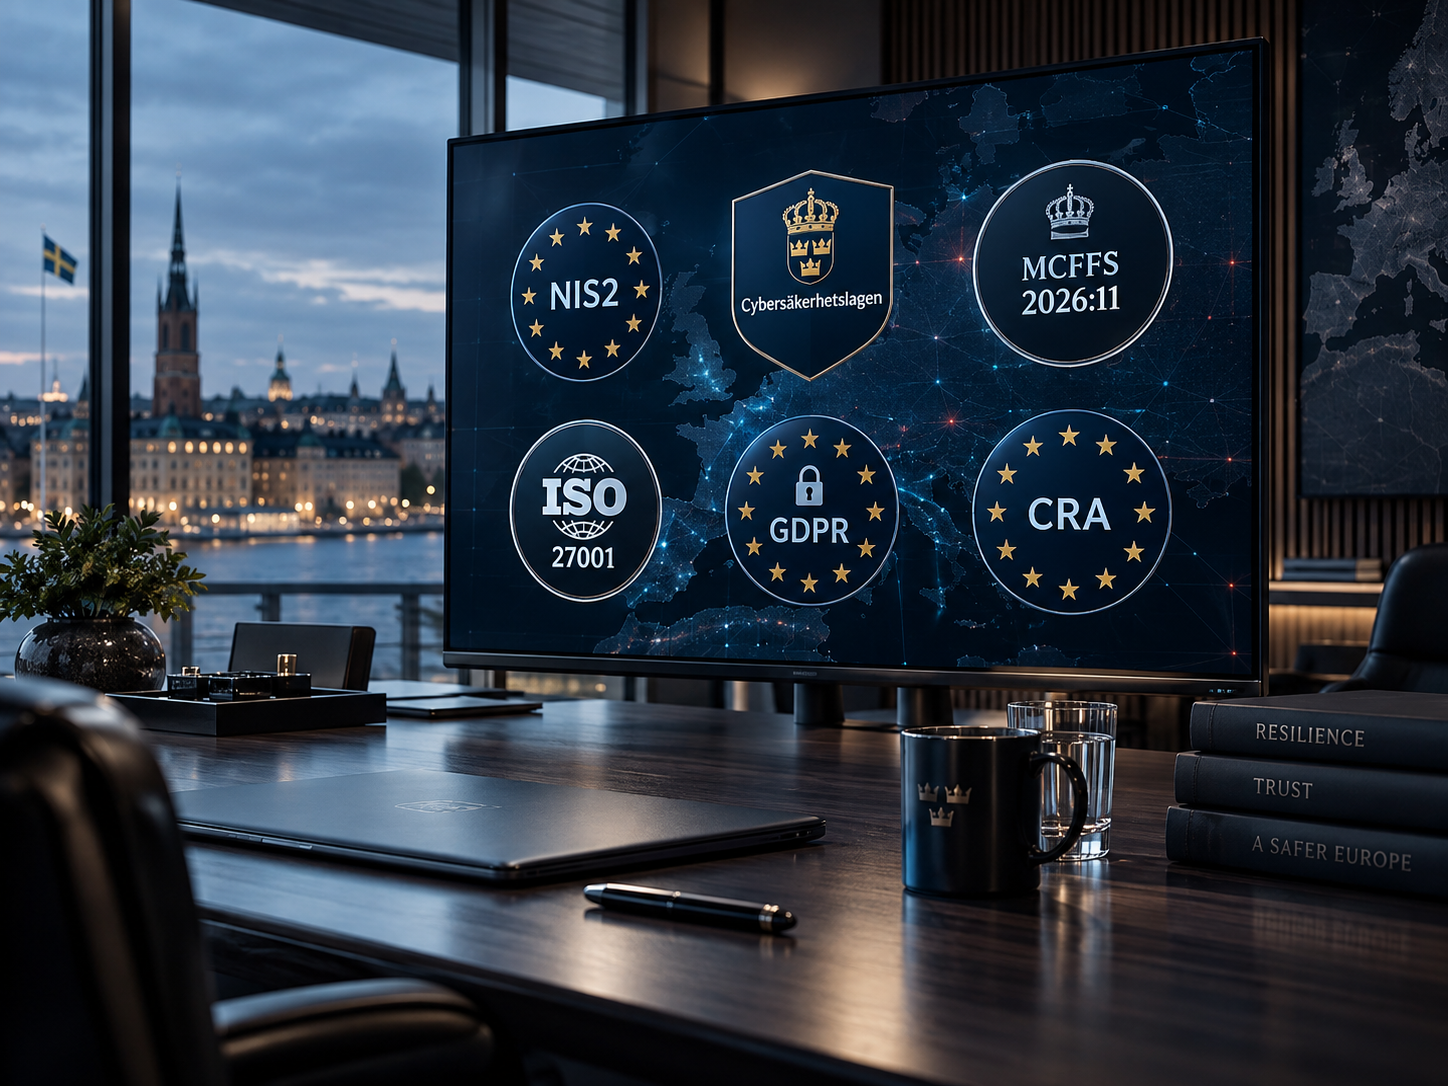
NIS2Swedish Cybersecurity ActMCFFS 2026:11ISO 27001CRA
NIS2, Swedish Cybersecurity Act, ISO 27001 and CRA
SIT CYBERBLICK

How well do you understand
your cybersecurity posture?

Answer 15 simple questions to get a clear view of your strengths and concrete recommendations for improvement. SIT Cyberblick provides guidance and does not replace a technical security review or a formal compliance assessment.

SIT Cyberblick is currently available in Swedish.

QUICK SELF-ASSESSMENT

From questions to clear next steps.

15simple questions about your cybersecurity work
Instantresults with strengths and prioritized improvements
PDFsummary to bring to your next meeting

No email address is required to see the result or download the report.

What do you need
better control over?

Have you outsourced IT operations but kept the accountability? Do you want more from an already mature security program? Or do you need structure, prioritization and follow-up in place quickly?

Leadership and security team
ASSURANCE

You outsourced IT operations.
Not accountability.

Keep your own independent technical view of the risks that remain, what to fix first and what to follow up with your IT provider.

Explore Assurance →
Mature security team comparing technical risk results
OPTIMIZATION

You have already come a long way.
Now test whether you can go further.

Compare SIT with what you already use in your own IT environment. Same environment. Same conditions. Let the results decide.

Explore Optimization →
IT owner in a server environment
CONTROL

Get control.
Prioritize the right risks.
Get the work done.

Build a systematic security process with clear priorities, expert support and recurring automated control. You fix the right risks first and drive risk down over time.

Explore Control →

See the way in.
See what can be exploited inside.

SIT Xternal shows what the internet sees and where an attacker can gain an initial foothold. SIT Appliance shows the internal technical risk and possible attack chains. Together they give you one connected view.

SIT Appliance in an IT environment
SIT APPLIANCE

See what is actually inside.

Map the internal IP-reachable environment, identify products and versions, and see which risks and attack chains deserve priority.

Explore SIT Appliance →
External attack surface over a connected city
SIT XTERNAL

See what the internet actually sees.

Identify exposed systems and services, analyze relevant vulnerabilities and understand what can contribute to initial access.

Explore SIT Xternal →
INTERNET→XTERNAL→INITIAL FOOTHOLD→APPLIANCE→INTERNAL RISK

Follow what we focus on
before the breach.

Attack paths, prioritization, resilience and how recurring technical control turns into measurable security improvement.

Cybersecurity Awareness Month
OCTOBER 2026

Cybersecurity Awareness Month 2026

The right information, sharper priorities and recurring follow-up.

Read more →
Lindholmen Software Development Day
20 OCTOBER 2026 · GOTHENBURG

The Perfect Storm Before the Breach

Reachability, attack paths and prioritization before the breach.

Read more →
BSides Copenhagen
14 NOVEMBER 2026 · COPENHAGEN

A Security Baseline Is Not an Attack Path

Why a baseline is not enough when the attack path changes the priority.

Read more →

Want to know where the risks actually are
and what to fix first?

Tell us how your IT environment works today. We will show where SIT can give you stronger control, sharper prioritization and a better basis for security decisions.