Better information in.
Better decisions out.
SIT Appliance starts with what actually exists in the reachable environment: systems, services, products and versions. Then it adds vulnerability and threat context to determine what deserves attention first. SIT identifies relevant and critical vulnerabilities that other market-leading solutions miss. Our comparative tests also show that we complete scans in less than half the time.
Identify reachable systems, services, products and versions with high precision.
Match the observed environment against continuously updated vulnerability intelligence.
Combine technical severity, known exploits, CISA KEV, EPSS, active exploitation, attack chains and business criticality.
Focus teams on the Critical and High risks that should be fixed first.
Dedicated physical hardware.
Deeper technical insight.
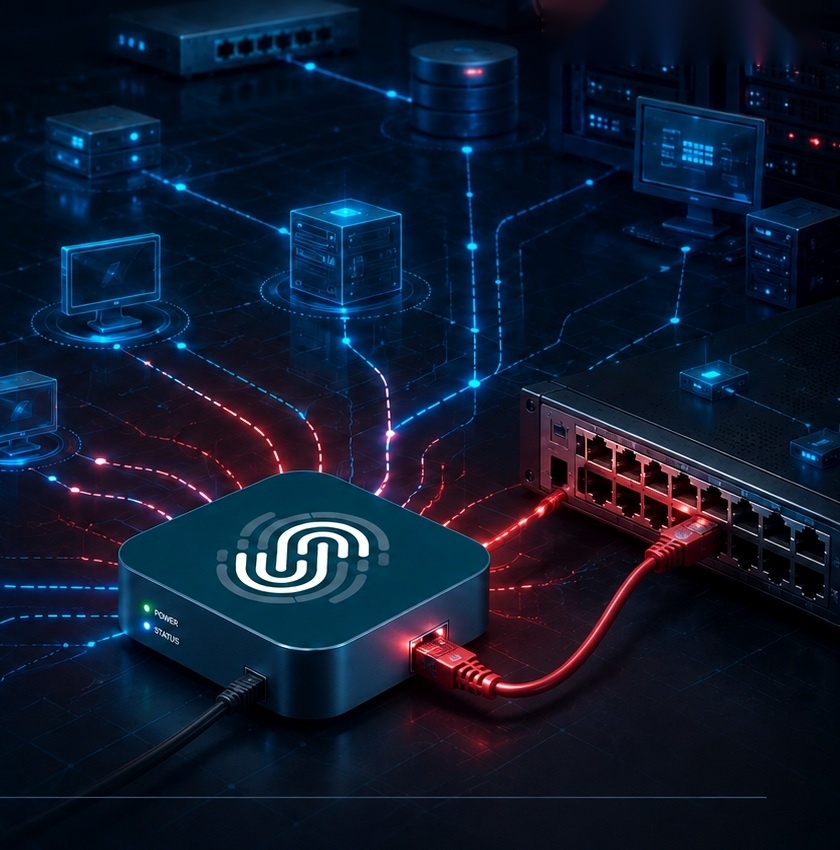
SIT Appliance’s dedicated physical hardware is part of our analysis method, not simply a delivery format. It provides consistent conditions for advanced fingerprinting and a more precise picture of systems, services, products and versions. It connects to your internal network and performs agentless, unauthenticated scans without privileged accounts. It provides a separate technical picture based on what the network actually reveals, without relying on credentials. No software is installed on your servers or endpoints, and no server capacity is required for our analysis engine.
Internal analysis stays local
Scan results, analyses, reports and history stay local in a hardened, locked-down and encrypted SIT Appliance. No information leaves your network. Recurring scans, Delta Report and Risk Index history let you track and demonstrate how risk is reduced over time and provide traceable evidence of a systematic security process.
Proactive control before an incident
SIT Appliance provides proactive technical control before an incident. It shows when the technical conditions for a breach exist without carrying out the breach, enabling automated, unattended control in production with low operational risk. The agreed IP-based systems include other sites, IT providers and cloud environments when Appliance reaches them from its network position.